
Why this matters
Most people should use the installation script. It does everything on this page in one run, it's tested on every release, and it's the quickest way to a working instance. This article is for the cases where you can't or won't run a script as root on a production server: your change process wants to review each command, your hardening baseline already owns Apache or MySQL, or you're building an image and need to know exactly what goes into it.
The steps follow the script's own order and settings, and they were run start to finish on a clean Red Hat Enterprise Linux 10.3 server for this release. If something here and the script ever disagree, the script wins, because it's the thing CI exercises. (One deliberate exception, in Step 5, is called out where it happens.)
RHEL differs from the Ubuntu guide in three ways that matter. PHP and MySQL both come from outside RHEL's own repositories: PHP 8.5 from the Remi repository, and MySQL 8.4 LTS from MySQL's Community repository. SELinux stays in enforcing mode, so the application's files and logs need the right labels. And the account that runs Apache is apache, not www-data.
CentOS Stream 10. The scripted installer treats CentOS Stream 10 and RHEL 10 as one code path, and the steps below are the same. This guide was run on RHEL. The difference is package access: RHEL needs a Red Hat subscription (or a cloud image that includes access to Red Hat's repositories) so that dnf can reach them, while CentOS Stream needs nothing extra.
Before you start
- A RHEL 10 server with at least 2 GB of memory, a static address or a DNS name, and outbound internet access. This guide was run on RHEL 10.3. Sizing guidance is in System Requirements.
- Working package access. Either a subscription registered with
subscription-manager, or a cloud image that brings its own. Rundnf repolistbefore you go on; it should list RHEL's BaseOS and AppStream repositories. - A root shell. Every command below runs as root. Start one with
sudo -iand stay in it. Step 5 relies on root's home directory, so asudoin front of each command won't do. - Ports 80 and 443 reachable from the people who'll use SimpleRisk. Step 10 opens them on the server's own firewall. Cloud security groups and network firewalls are yours to adjust.
- A hostname for the instance. Throughout this article, replace
{your-simplerisk-host}with your instance's hostname (for example,grc.example.com). It's a hostname only: nohttps://, no path. - SELinux left in enforcing mode. The steps below configure it properly. Switching it to permissive to "get past a problem" hides the symptom of a wrong label, and the problem comes back when you switch it on again.
- A decision about the TLS certificate. Apache creates a self-signed certificate the first time it starts, so the site comes up on HTTPS right away. Browsers will warn about it. Replace it before real users arrive, using HTTPS and TLS Configuration.
Step-by-step
1. Update the system and add the repositories
dnf -y update
dnf -y install wget firewalld
Add MySQL's repository and import its signing key. The release package enables MySQL's newest series by default; Step 3 pins the 8.4 long-term-support series that SimpleRisk is tested on.
rpm -Uvh https://dev.mysql.com/get/mysql84-community-release-el10-2.noarch.rpm
rpm --import https://repo.mysql.com/RPM-GPG-KEY-mysql-2025
Add EPEL, then the Remi repository that carries PHP 8.5, importing Remi's key before you install its release package. The script installs EPEL as well, so this guide does too.
dnf -y install https://dl.fedoraproject.org/pub/epel/epel-release-latest-10.noarch.rpm
rpm --import https://rpms.remirepo.net/RPM-GPG-KEY-remi2025
dnf -y install https://rpms.remirepo.net/enterprise/remi-release-10.rpm
dnf -y update
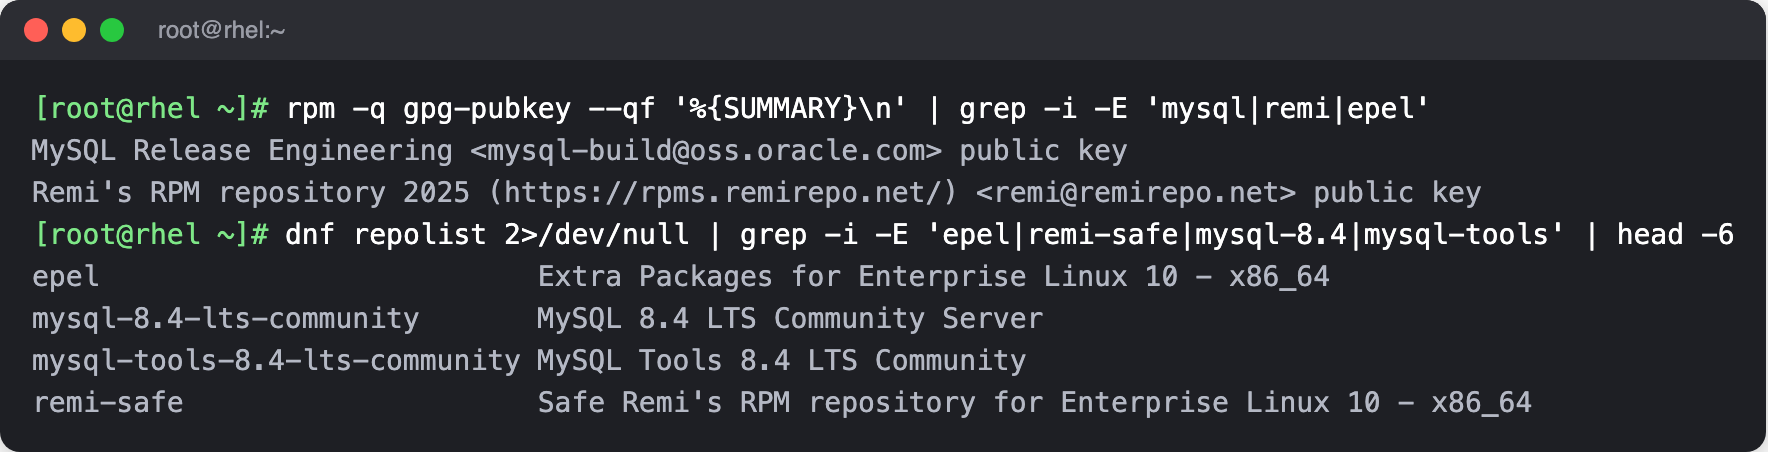
Check what you added.
rpm -q gpg-pubkey --qf '%{SUMMARY}\n' | grep -i -E 'mysql|remi|epel'
dnf repolist 2>/dev/null | grep -i -E 'epel|remi-safe|mysql-8.4|mysql-tools' | head -6
The first command lists the MySQL and Remi signing keys. Before you rely on them, compare their fingerprints with the ones each project publishes. The second lists the repositories, including mysql-8.4-lts-community and remi-safe.
2. Install PHP and Apache
Switch the PHP module stream to Remi's 8.5 build, then install Apache and PHP with the extensions SimpleRisk needs.
dnf -y module reset php
dnf -y module enable php:remi-8.5
dnf -y install httpd php php-cli php-common php-mysqlnd php-mbstring php-opcache \
  php-gd php-zip php-json php-ldap php-curl php-xml php-intl php-process
The php package includes the Apache module, so PHP runs inside Apache. That matters in Step 6.
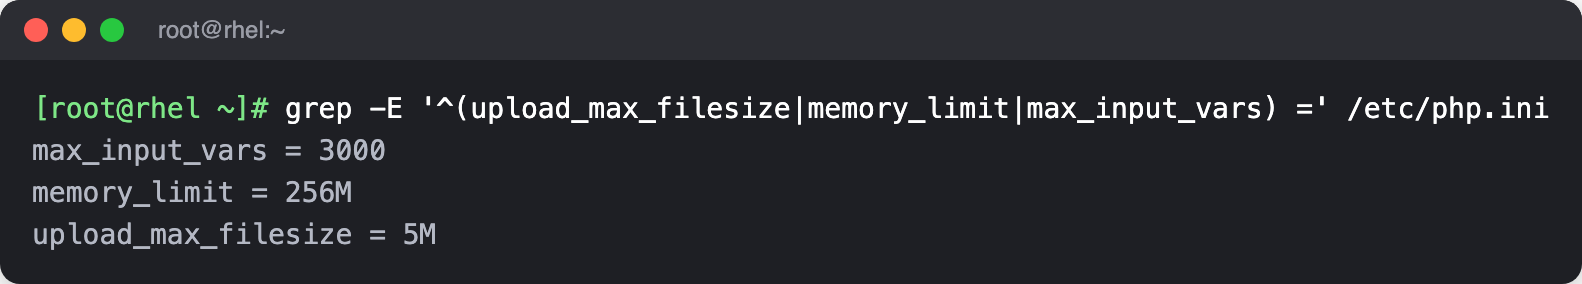
The script sets a 5 MB upload limit, a 256 MB memory limit, and room for 3,000 input variables. The last one matters on pages that post many fields at once, because PHP drops any field past the limit.
sed -i 's/^\(upload_max_filesize =\).*/\1 5M/; s/^\(memory_limit =\).*/\1 256M/; s/^;\?\(max_input_vars =\).*/\1 3000/' /etc/php.ini
grep -E '^(upload_max_filesize|memory_limit|max_input_vars) =' /etc/php.ini
The grep should print the three values you just set. If one is missing, the file has a different layout than expected and you'll need to set it by hand.
3. Install MySQL and the remaining packages
Install the MySQL 8.4 server from MySQL's repository. The --disablerepo and --enablerepo pair pins the 8.4 series, and the two --exclude options keep RHEL's own database packages (MariaDB, and MySQL 8.4 from AppStream where it exists) from being pulled in beside it.
dnf install -y mysql-community-server --exclude 'mariadb*' --exclude 'mysql8.4*' \
  --disablerepo='mysql-*' --enablerepo='mysql-8.4-lts-community'
systemctl enable --now mysqld
Then the packages around it. mod_ssl gives Apache HTTPS, iputils provides the ping command that asset discovery uses, and cronie runs the scheduled job in Step 7. The script also installs sendmail so the server can send mail locally. If you'll send mail through an SMTP server instead, you can leave out sendmail, sendmail-cf, and m4, and skip the sendmail lines in Step 9.
dnf -y install mod_ssl iputils sendmail sendmail-cf m4 cronie
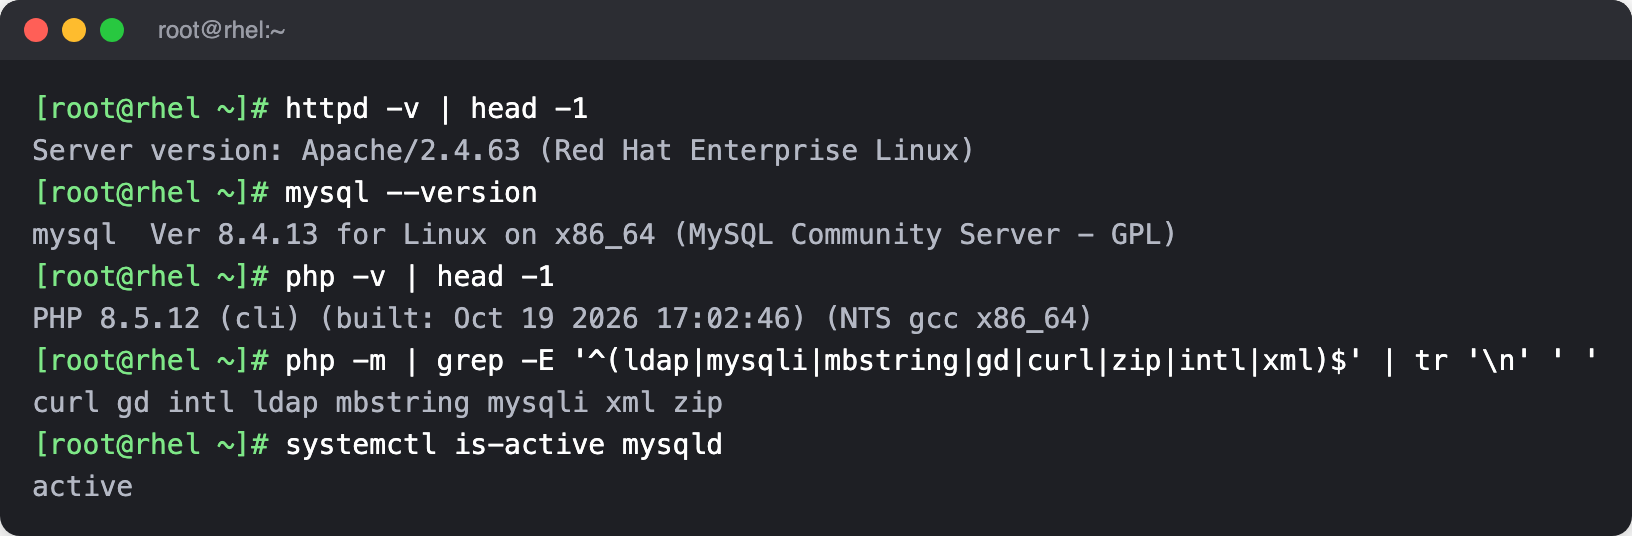
Check what you got.
httpd -v | head -1
mysql --version
php -v | head -1
php -m | grep -E '^(ldap|mysqli|mbstring|gd|curl|zip|intl|xml)$' | tr '\n' ' '
systemctl is-active mysqld
4. Download SimpleRisk and verify it
SimpleRisk publishes the current version and the checksum of each download in one small file. Read the version and both checksums from it, download, and check.
RELEASES=$(curl -fsSL https://updates.simplerisk.com/releases.xml)
VERSION=$(printf '%s' "$RELEASES" | grep -oP '

   \K[^<]+' | head -n1) DB_SHA=$(printf '%s' "$RELEASES" | sed -n '/

    /,/<\/en>/p' | grep -oP '

     \K[^<]+' | head -n1) echo "Installing SimpleRisk $VERSION"
Download the application bundle, check it, and unpack it into /var/www.
cd /var/www
wget "https://simplerisk-downloads.s3.amazonaws.com/public/bundles/simplerisk-${VERSION}.tgz"
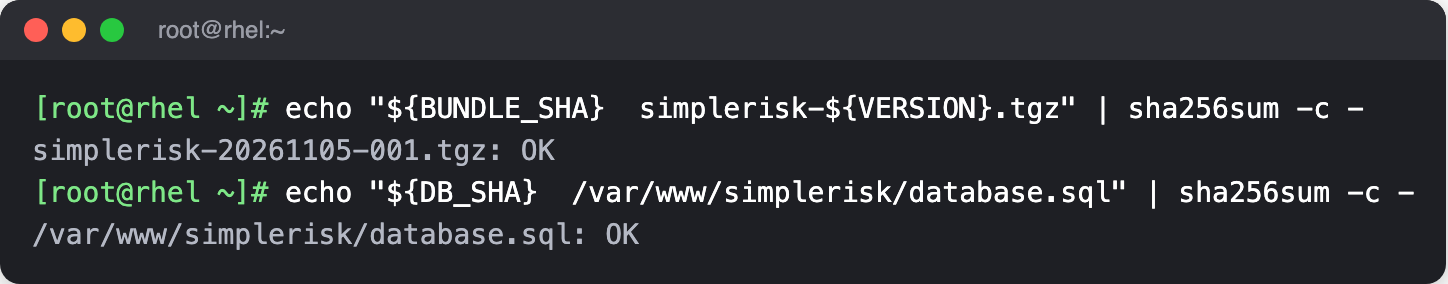
echo "${BUNDLE_SHA}  simplerisk-${VERSION}.tgz" | sha256sum -c -
tar -xzf "simplerisk-${VERSION}.tgz"
rm "simplerisk-${VERSION}.tgz"
sha256sum must print OK. If it prints FAILED, delete the file and start again; don't unpack it. Download the English database file the same way.
wget -O /var/www/simplerisk/database.sql \
  "https://github.com/simplerisk/database/raw/master/simplerisk-en-${VERSION}.sql"
echo "${DB_SHA}  /var/www/simplerisk/database.sql" | sha256sum -c -
Both checks print OK, with the version you downloaded in the first filename.
Create the configuration file from the sample, and give Apache's account ownership of the application directory.
cp /var/www/simplerisk/includes/config.sample.php /var/www/simplerisk/includes/config.php
chown -R apache: /var/www/simplerisk
5. Create the database and connect SimpleRisk to it
The MySQL package creates the root account with a temporary password, already expired, and writes it to MySQL's log. Unlike on Ubuntu, root can't just connect over the local socket without one. Read it, then replace it with a password of your own.
TEMP=$(grep 'temporary password' /var/log/mysqld.log | tail -n 1 | awk '{print $NF}')
ROOTPASS="$(openssl rand -hex 16)-Aa1"
mysql -u root --password="$TEMP" --connect-expired-password \
  -e "ALTER USER 'root'@'localhost' IDENTIFIED BY '${ROOTPASS}'"
MySQL's default password policy wants mixed case, a digit, and a special character. The -Aa1 on the end guarantees all three, so the generated password passes. Store it where mysql can read it, so the commands that follow don't need a password typed into them.
printf '[client]\nuser=root\npassword=%s\n' "$ROOTPASS" > /root/.my.cnf
chmod 600 /root/.my.cnf
mysql reads that file from root's home directory, which is why "Before you start" asked for a real root shell. If you want a copy of the root password in your password manager, print it with echo "$ROOTPASS" before you close the shell.
Create the database and a dedicated user with its own generated password, import the schema, and grant the user the permissions SimpleRisk needs.
DBPASS="$(openssl rand -hex 16)-Aa1"
mysql -e "CREATE DATABASE simplerisk"
mysql -e "CREATE USER 'simplerisk'@'localhost' IDENTIFIED BY '${DBPASS}'"
mysql simplerisk < /var/www/simplerisk/database.sql
mysql -e "GRANT SELECT, INSERT, UPDATE, DELETE, CREATE, DROP, REFERENCES, INDEX, ALTER ON simplerisk.* TO 'simplerisk'@'localhost'"
Write the connection details into the configuration file, then delete the schema file, which has no further use.
sed -i "s/\(DB_HOSTNAME', '\)__DB_HOSTNAME__/\1127.0.0.1/; s/\(DB_PORT', '\)__DB_PORT__/\13306/; s/\(DB_USERNAME', '\)__DB_USERNAME__/\1simplerisk/; s/\(DB_PASSWORD', '\)__DB_PASSWORD__/\1${DBPASS}/; s/\(DB_DATABASE', '\)__DB_DATABASE__/\1simplerisk/; s/\(USE_DATABASE_FOR_SESSIONS', '\)__USE_DATABASE_FOR_SESSIONS__/\1true/" \
  /var/www/simplerisk/includes/config.php
rm /var/www/simplerisk/database.sql
The database password now lives only in config.php. If you want a copy for your password manager, print it with echo "$DBPASS" before you close the shell.
Now MySQL's own settings. The script sets the SQL mode to ERROR_FOR_DIVISION_BY_ZERO,NO_ENGINE_SUBSTITUTION, which drops MySQL's strict defaults, and it raises the password policy for any password set later: at least 20 characters, with at least one uppercase letter, one lowercase letter, and one digit, and no username inside the password. Add both to /etc/my.cnf and restart MySQL.
cat >> /etc/my.cnf <<'EOF'

# SimpleRisk
sql_mode=ERROR_FOR_DIVISION_BY_ZERO,NO_ENGINE_SUBSTITUTION
loose-validate_password.policy=MEDIUM
loose-validate_password.length=20
loose-validate_password.mixed_case_count=1
loose-validate_password.number_count=1
loose-validate_password.special_char_count=0
loose-validate_password.check_user_name=ON
EOF
systemctl restart mysqld
The scripted installer writes these same settings to /etc/my.cnf. An earlier version of the script put them in a separate file under /etc/my.cnf.d/, which the MySQL Community package doesn't read, so MySQL ignored the file and fell back to its strict defaults after any restart. On a test server the result was that SimpleRisk's scheduled job logged Incorrect DATE value: '0000-00-00' every minute. If you installed with an older copy of the script, run the checks below after a restart and add the settings to /etc/my.cnf if they're missing.
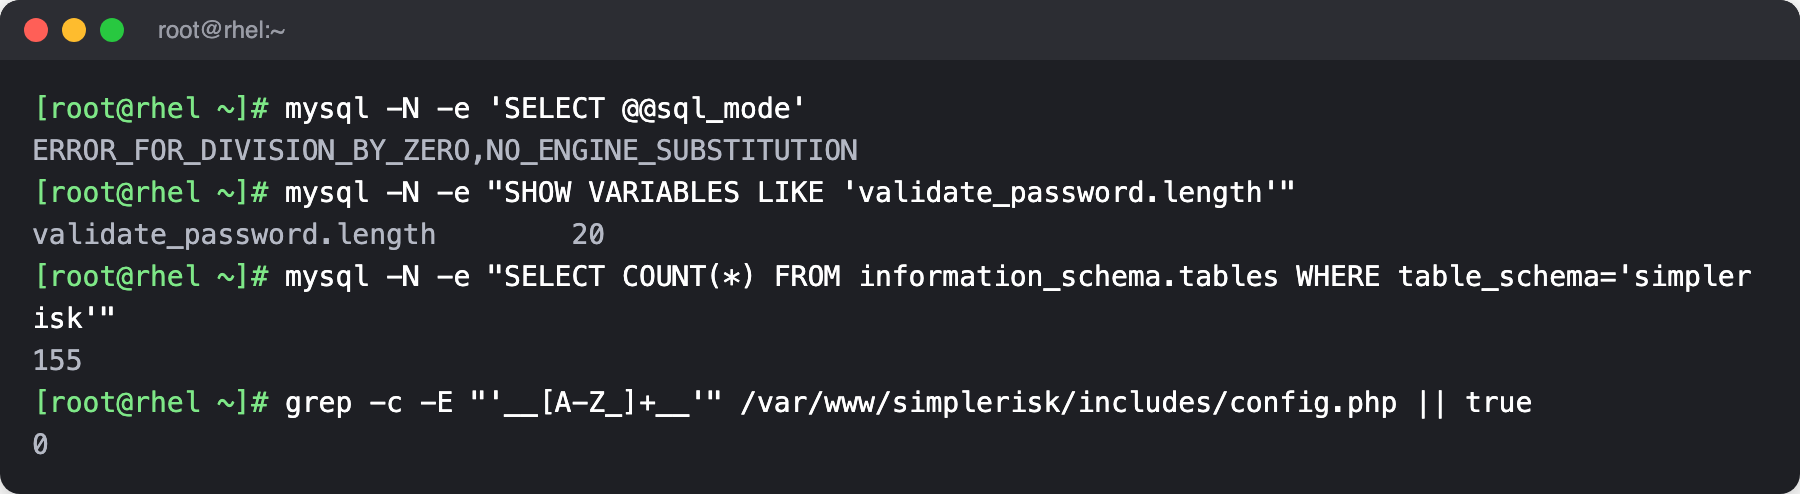
Check the result.
mysql -N -e 'SELECT @@sql_mode'
mysql -N -e "SHOW VARIABLES LIKE 'validate_password.length'"
mysql -N -e "SELECT COUNT(*) FROM information_schema.tables WHERE table_schema='simplerisk'"
grep -c -E "'__[A-Z_]+__'" /var/www/simplerisk/includes/config.php
The SQL mode should read exactly as above, the password length 20, the table count a number above zero (155 when this guide was verified), and the last line 0, meaning no __PLACEHOLDER__ value is left in the file.
6. Point Apache at SimpleRisk
Turn off Apache's default welcome page, and point the HTTPS site at SimpleRisk's directory.
mv /etc/httpd/conf.d/welcome.conf /etc/httpd/conf.d/welcome.conf.disabled
sed -i 's|#\?\(DocumentRoot "/var/www/\)html"|\1simplerisk"|' /etc/httpd/conf.d/ssl.conf
Add a site that serves SimpleRisk on port 80 and sends every request to HTTPS. The Directory block outside it applies to both sites. SimpleRisk relies on .htaccess files to protect its own directories, so Apache has to honor them, and the block also switches off directory listings.
cat > /etc/httpd/conf.d/simplerisk.conf <<'EOF'


    DocumentRoot "/var/www/simplerisk/" RewriteEngine On RewriteCond %{HTTPS} !=on RewriteRule ^/?(.*) https://%{SERVER_NAME}/$1 [R,L]


    AllowOverride All Require all granted Options -Indexes

EOF
PHP runs as an Apache module here, and that module needs the prefork processing model. RHEL's Apache defaults to the event model, so switch.
sed -i 's/#\(LoadModule mpm_prefork\)/\1/; s/\(LoadModule mpm_event\)/#\1/' /etc/httpd/conf.modules.d/00-mpm.conf
7. Create the log directory and the scheduled job
SimpleRisk writes its application log to /var/log/simplerisk. The directory belongs to Apache's account, with no access for anyone else.
mkdir -p /var/log/simplerisk
touch /var/log/simplerisk/simplerisk.log
chown -R apache: /var/log/simplerisk
chmod 750 /var/log/simplerisk
chmod 640 /var/log/simplerisk/simplerisk.log
The scheduled job runs every minute as Apache's account, never as root. It's what sends notifications, runs queued background work, and takes backups, so a missing job shows up as features that quietly never fire. See The Cron Jobs for what it does.
echo "* * * * * apache $(which php) -f /var/www/simplerisk/cron/cron.php" > /etc/cron.d/simplerisk
chmod 644 /etc/cron.d/simplerisk
8. Configure SELinux
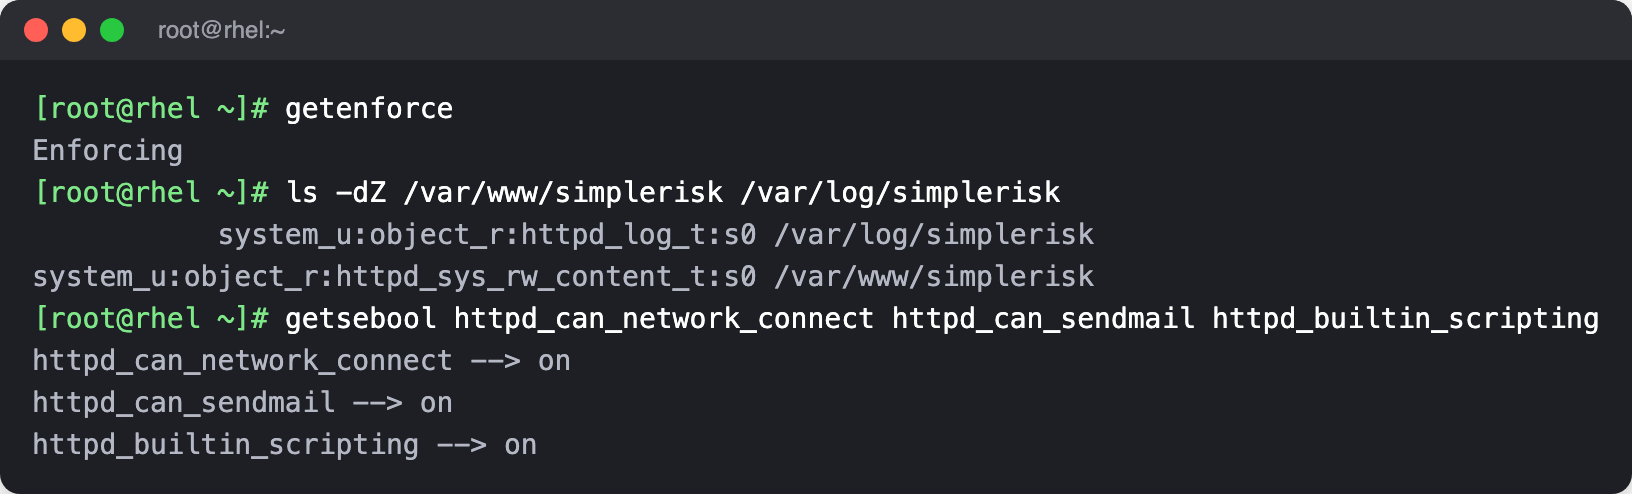
Check that SELinux is enforcing, which is how RHEL ships.
getenforce
Apache needs a few SELinux permissions to do what SimpleRisk asks of it. The script turns seven on; two of them (httpd_builtin_scripting and httpd_enable_cgi) were already on in a fresh RHEL 10 install, and the other five were off. The -P makes each change survive a reboot.
for b in httpd_builtin_scripting httpd_can_network_connect httpd_can_sendmail httpd_dbus_avahi \
         httpd_enable_cgi httpd_read_user_content httpd_tty_comm; do
  setsebool -P $b=1
done
The script also sets 26 other Apache permissions to off. On a fresh RHEL 10 system every one of them was already off, so this loop only matters if your hardening baseline turned any on. Run it if you want the same end state as the script.
for b in allow_httpd_anon_write allow_httpd_mod_auth_ntlm_winbind allow_httpd_mod_auth_pam \
         allow_httpd_sys_script_anon_write httpd_can_check_spam httpd_can_network_connect_cobbler \
         httpd_can_network_connect_db httpd_can_network_memcache httpd_can_network_relay \
         httpd_dbus_sssd httpd_enable_ftp_server httpd_enable_homedirs httpd_execmem httpd_manage_ipa \
         httpd_run_preupgrade httpd_run_stickshift httpd_serve_cobbler_files httpd_setrlimit \
         httpd_ssi_exec httpd_tmp_exec httpd_use_cifs httpd_use_fusefs httpd_use_gpg httpd_use_nfs \
         httpd_use_openstack httpd_verify_dns; do
  setsebool -P $b=0
done
Then label the files. The application directory has to be writable by Apache, and the log directory is labelled as Apache's log location.
chcon -R -t httpd_sys_rw_content_t /var/www/simplerisk
chcon -R -t httpd_log_t /var/log/simplerisk
Check the labels and the permissions.
getenforce
ls -dZ /var/www/simplerisk /var/log/simplerisk
getsebool httpd_can_network_connect httpd_can_sendmail httpd_builtin_scripting
9. Start the services
Start the scheduled-job service and Apache, and make both start at boot. The first start is also when Apache creates its self-signed certificate.
systemctl enable --now crond httpd
If you installed sendmail, the script adds the server's hostname to the localhost line of /etc/hosts and then starts it. This command edits the file once, so don't repeat it.
sed -i "s/\(localhost\)/\1 $(hostname)/g" /etc/hosts
systemctl start sendmail
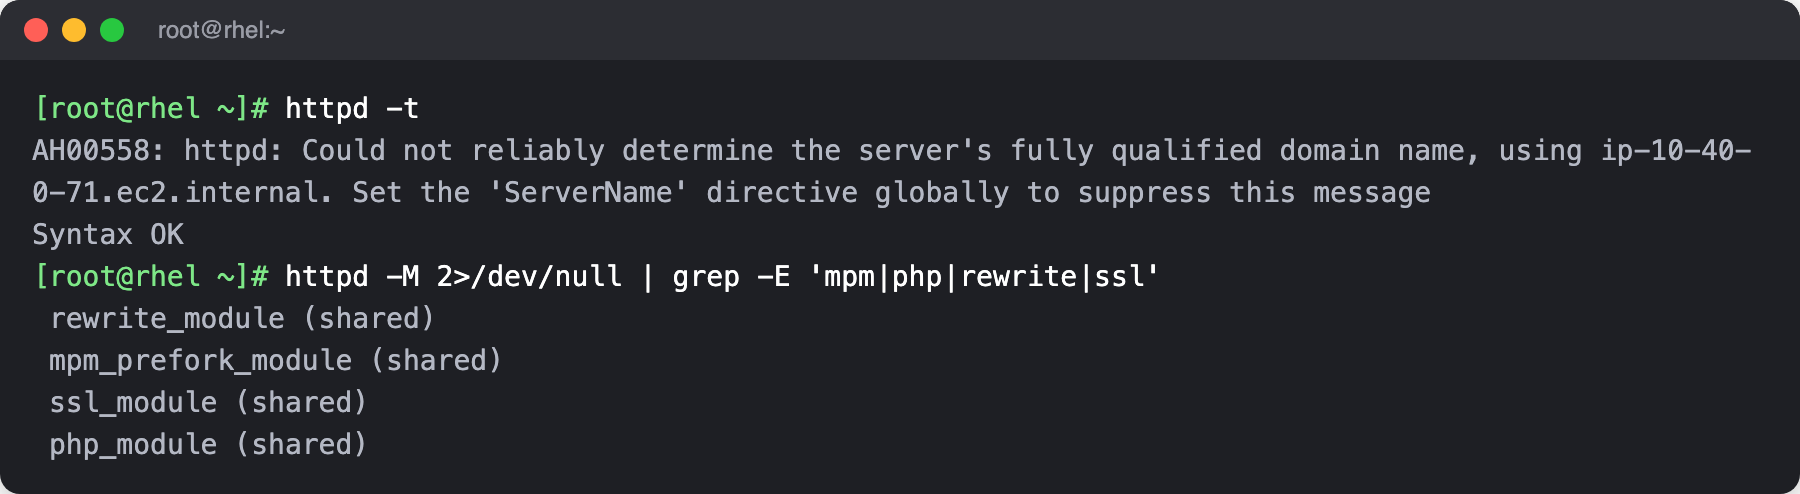
Test Apache's configuration and check which modules loaded.
httpd -t
httpd -M 2>/dev/null | grep -E 'mpm|php|rewrite|ssl'
Syntax OK is what matters. Above it you'll see a warning that Apache couldn't work out the server's fully qualified domain name. It's harmless, and it goes away if you add ServerName {your-simplerisk-host} to /etc/httpd/conf.d/simplerisk.conf. The module list should show mpm_prefork_module, php_module, rewrite_module, and ssl_module.
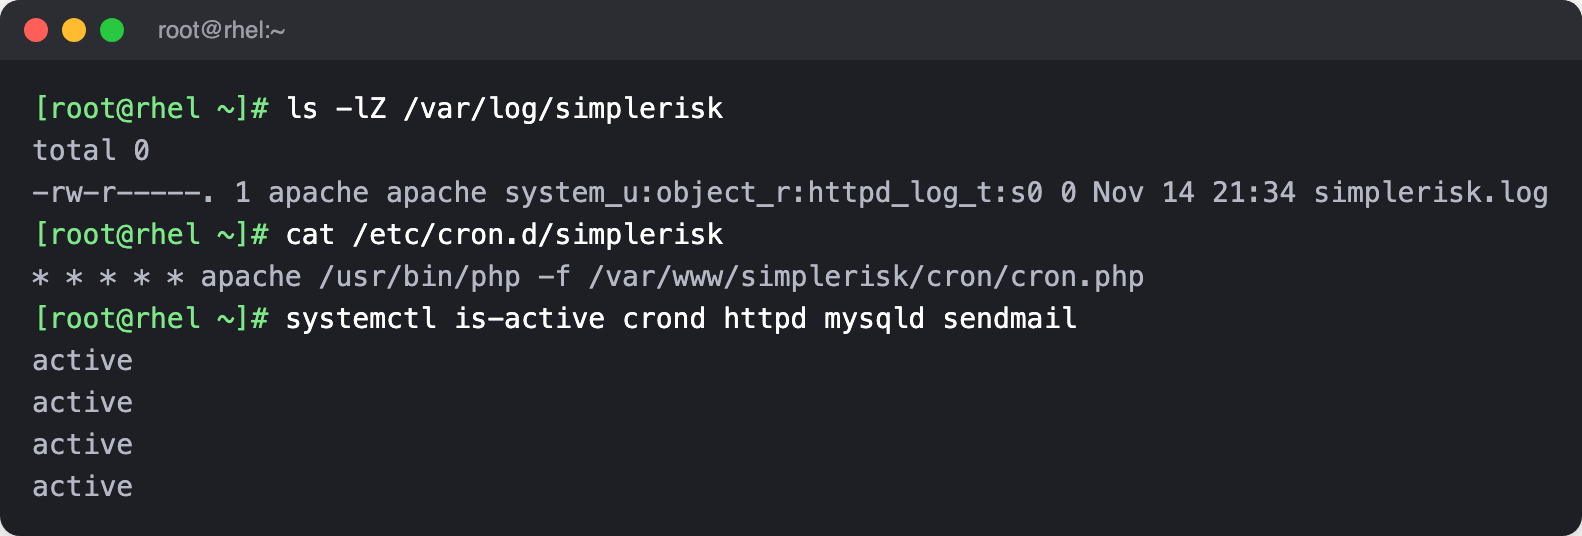
Confirm the log file, the scheduled job, and the services.
ls -lZ /var/log/simplerisk
cat /etc/cron.d/simplerisk
systemctl is-active crond httpd mysqld sendmail
10. Open the firewall
Start the firewall, allow the three services, and reload.
systemctl enable --now firewalld
firewall-cmd --permanent --zone=public --add-service=http
firewall-cmd --permanent --zone=public --add-service=https
firewall-cmd --permanent --zone=public --add-service=ssh
firewall-cmd --reload
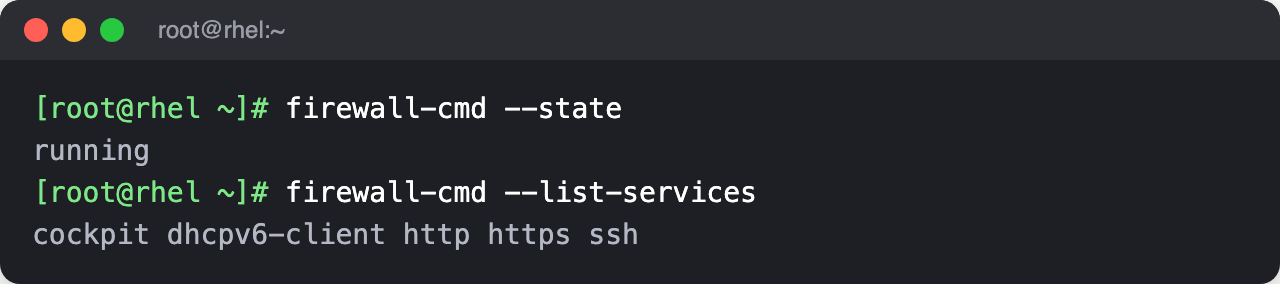
firewall-cmd --state
firewall-cmd --list-services
If the first firewall-cmd complains that FirewallD isn't running, wait a few seconds and run it again; the script polls for up to 30 seconds for the same reason. The list should include http, https, and ssh. It will also show cockpit and dhcpv6-client, which RHEL's default zone allows. Nothing listens on the Cockpit port unless you enable Cockpit, but remove it from the zone if your baseline says to.
11. Check the install, then finish in the browser
From the server, confirm both ports answer. The -k accepts the self-signed certificate.
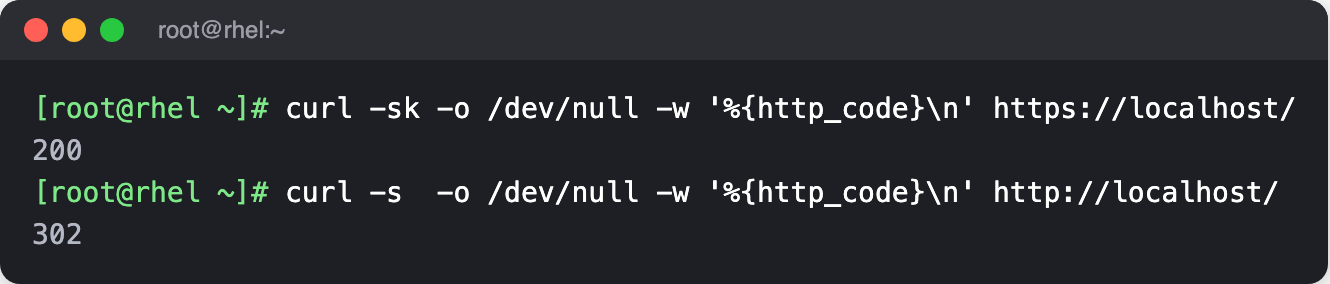
curl -sk -o /dev/null -w '%{http_code}\n' https://localhost/
curl -s  -o /dev/null -w '%{http_code}\n' http://localhost/
The first should print 200 and the second a redirect code such as 302.
Now open https://{your-simplerisk-host}/ in a browser. It will warn that the certificate isn't trusted, because of the self-signed certificate; accept it for now and replace the certificate when you reach HTTPS and TLS Configuration.
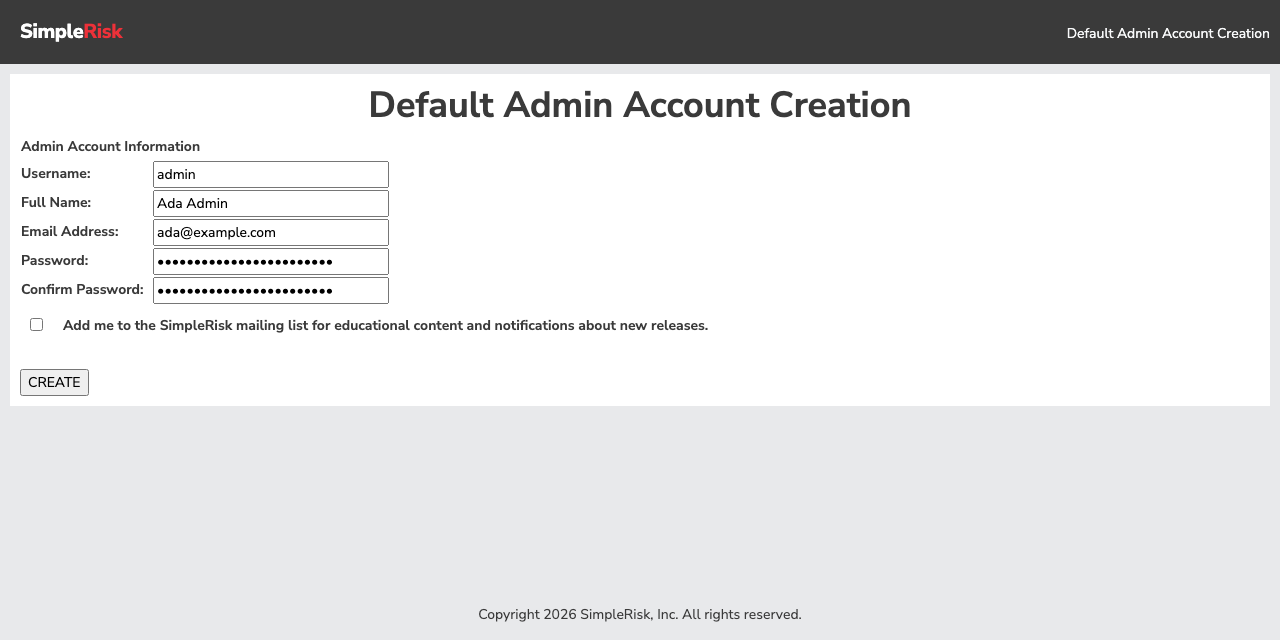
You won't see the installation wizard described in The Initial Configuration Wizard. The database and config.php are already in place, so SimpleRisk goes straight to creating the first administrator. Enter a username, your full name, an email address, and a strong password, twice. The mailing-list box is optional and starts unticked. Select CREATE.
SimpleRisk then shows the login page. Sign in with the account you just created.
You land on the Home dashboard, with a Welcome to SimpleRisk card that lists the first steps. The counters read zero because nothing has been entered yet.
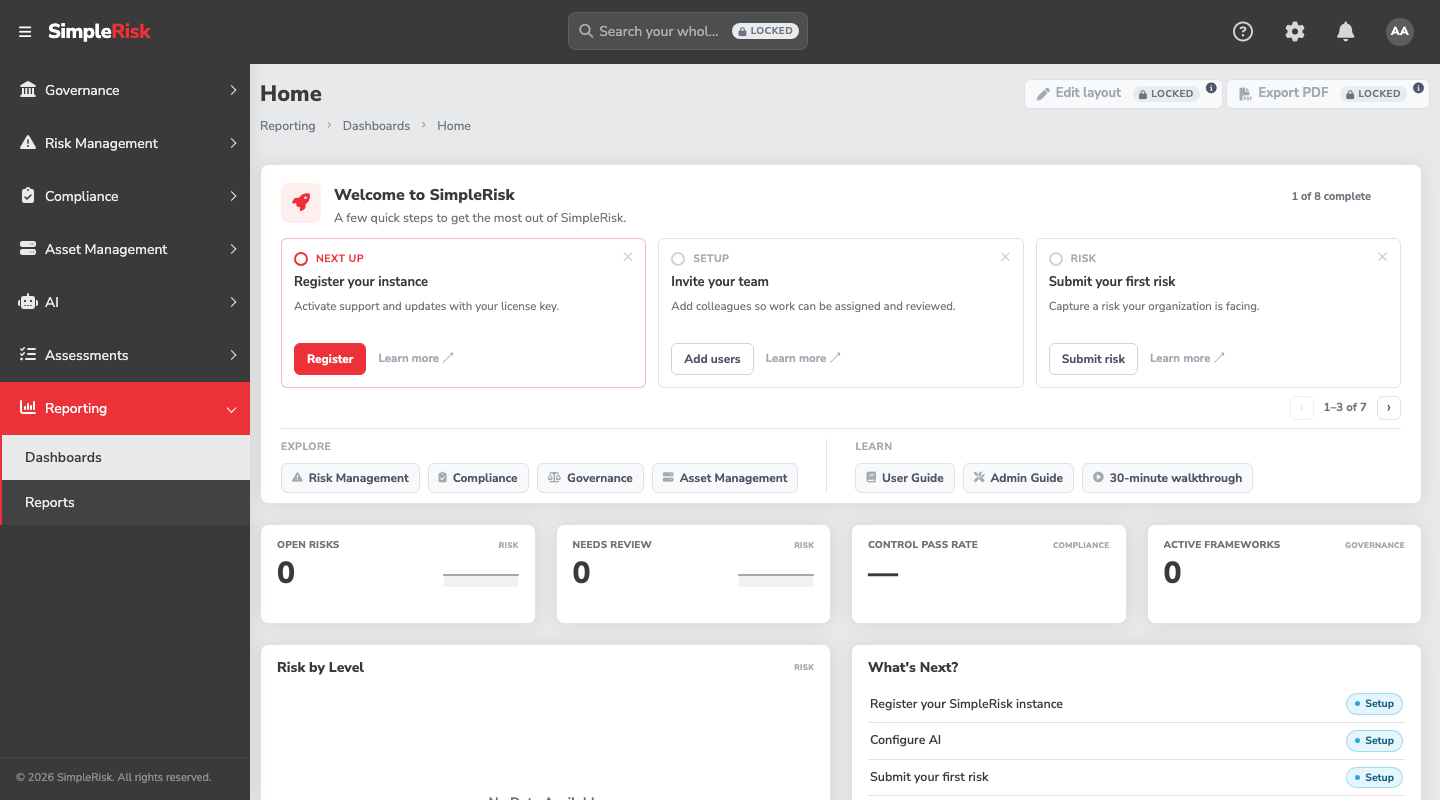
From here, register the instance so it can receive updates, following Registration and Licensing.
Common pitfalls
- Labels that don't survive a relabel.
chconchanges a file's label, but a full relabel of the system, or arestoreconrun over these directories, resets them to the policy's defaults, and SELinux can then block Apache from writing where it needs to. If you want the labels to stick, add policy rules and apply them. These two commands produce the same labels as Step 8, and survive a relabel.
bash dnf -y install policycoreutils-python-utils semanage fcontext -a -t httpd_sys_rw_content_t '/var/www/simplerisk(/.*)?' semanage fcontext -a -t httpd_log_t '/var/log/simplerisk(/.*)?' restorecon -R /var/www/simplerisk /var/log/simplerisk
- Putting MySQL's settings in
/etc/my.cnf.d/. The MySQL Community package doesn't read that directory, so MySQL quietly runs with its strict defaults. Use/etc/my.cnf, and check the SQL mode with the commands at the end of Step 5 after every restart you care about. - Testing Apache's configuration before it has ever started. The HTTPS site points at a certificate file that Apache creates the first time it starts. Run
httpd -tbefore then, and it fails complaining thatlocalhost.crtdoesn't exist or is empty. Start Apache first, as Step 9 does. - Switching SELinux to permissive. It makes errors disappear, and it removes a layer of protection from a server that holds your risk data. If something is denied, look at what was blocked with
ausearch -m avc -ts recentand fix the label or the permission. On the verified install, that command found nothing. - Looking for the installation wizard. A manual install skips it, as the last step explains. The first thing you'll see is the administrator form.
- Uninstalling by deleting
/var/www/simplerisk. The scheduled job from Step 7 keeps firing every minute and can recreate the log directory behind you. Remove/etc/cron.d/simpleriskfirst.